Offensive security, built around real risk.
Expert-led pentesting, red teaming, product security, and vCISO advisory. Uncover exploitable risk, speed up remediation, and meet customer and compliance requirements.


Trusted by 400+ fast-growing tech teams.
From fast-growing startups to global enterprises.
Trusted by 400+ organizations worldwide.
Security expertise for every stage of growth
From your first pentest to an ongoing security program, Blaze brings together offensive security, product security, security engineering, and strategic advisory as your needs evolve.
Penetration Testing
Manual web, API, mobile, cloud, and network testing that finds the business-logic flaws scanners miss.
Red Team & Adversary Simulation
Goal-driven attacks that measure detection and response.
Product Security Assessment
Threat-model-first review across your architecture, code, and SDLC.
Microsoft 365 Security Assessment
An attacker's-eye review of your Entra ID and Microsoft 365 tenant.
Strategic, vCISO & Advisory
Expert security leadership that runs your questionnaires, policies, and compliance readiness.
Blaze Portal (PTaaS)
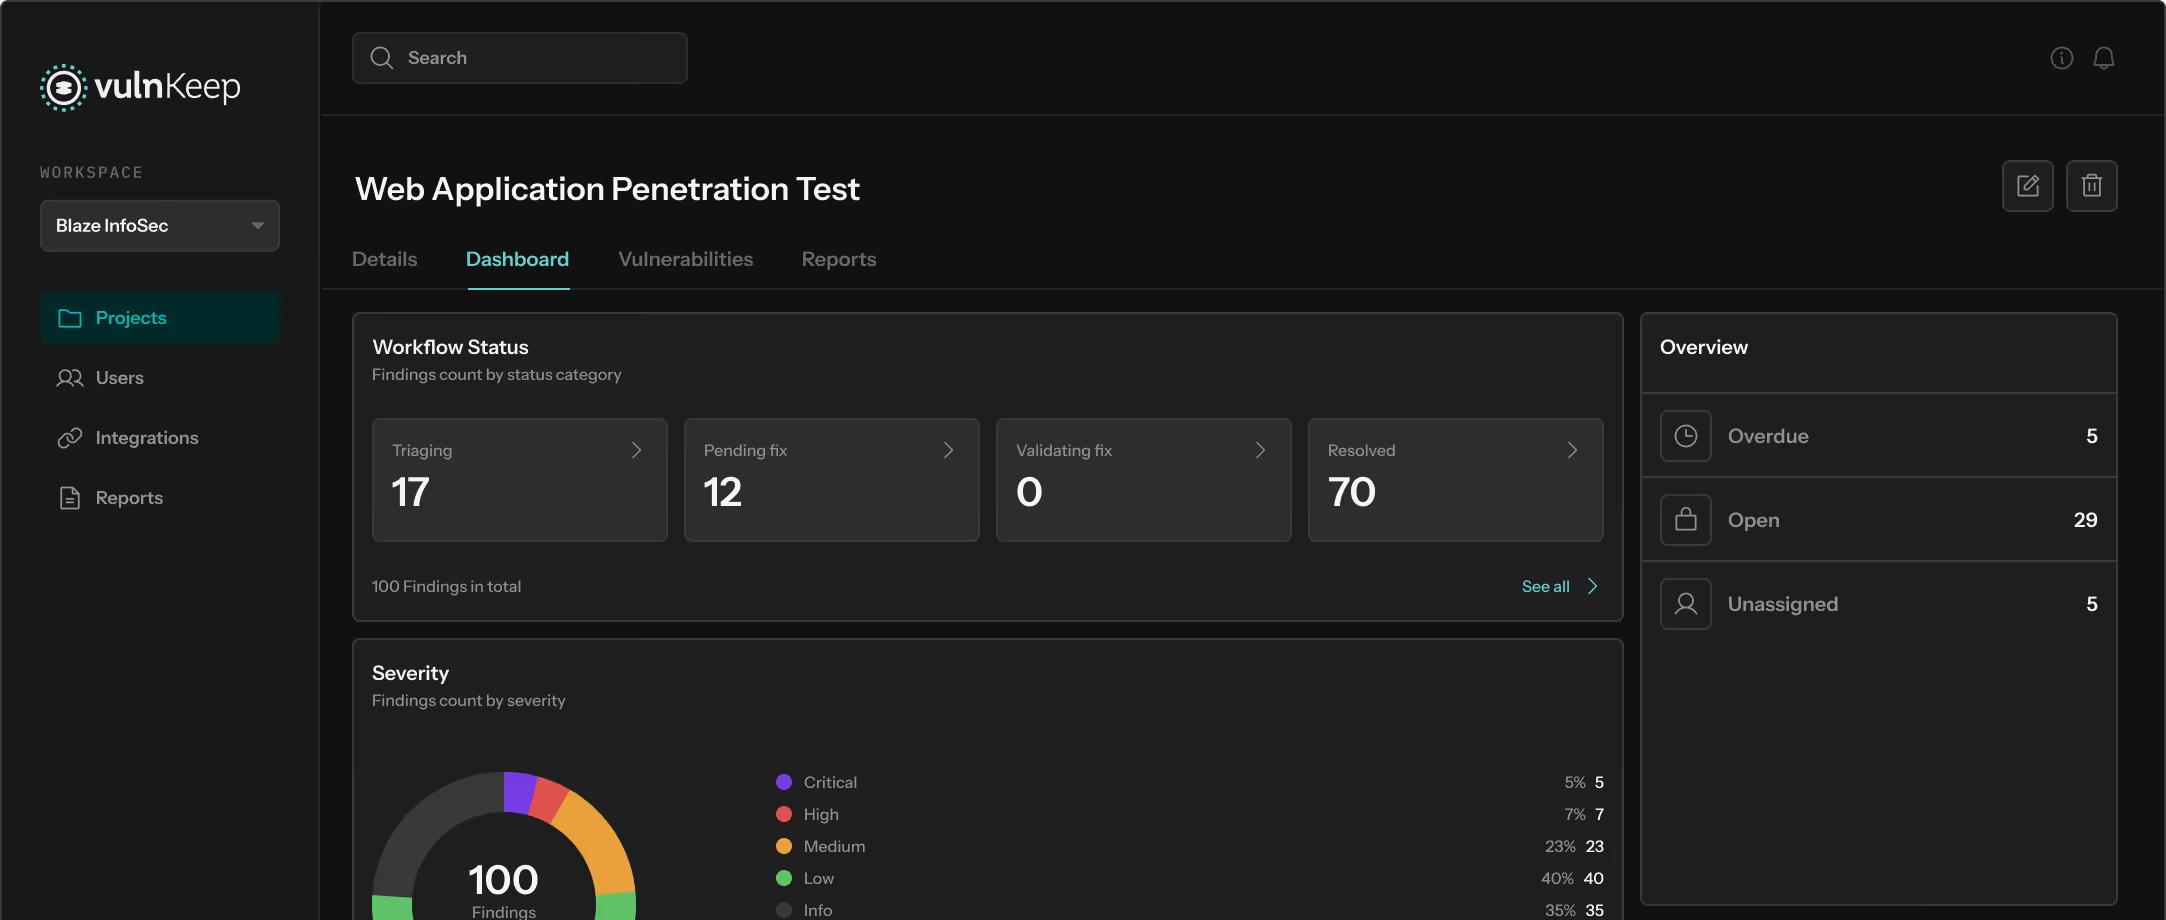
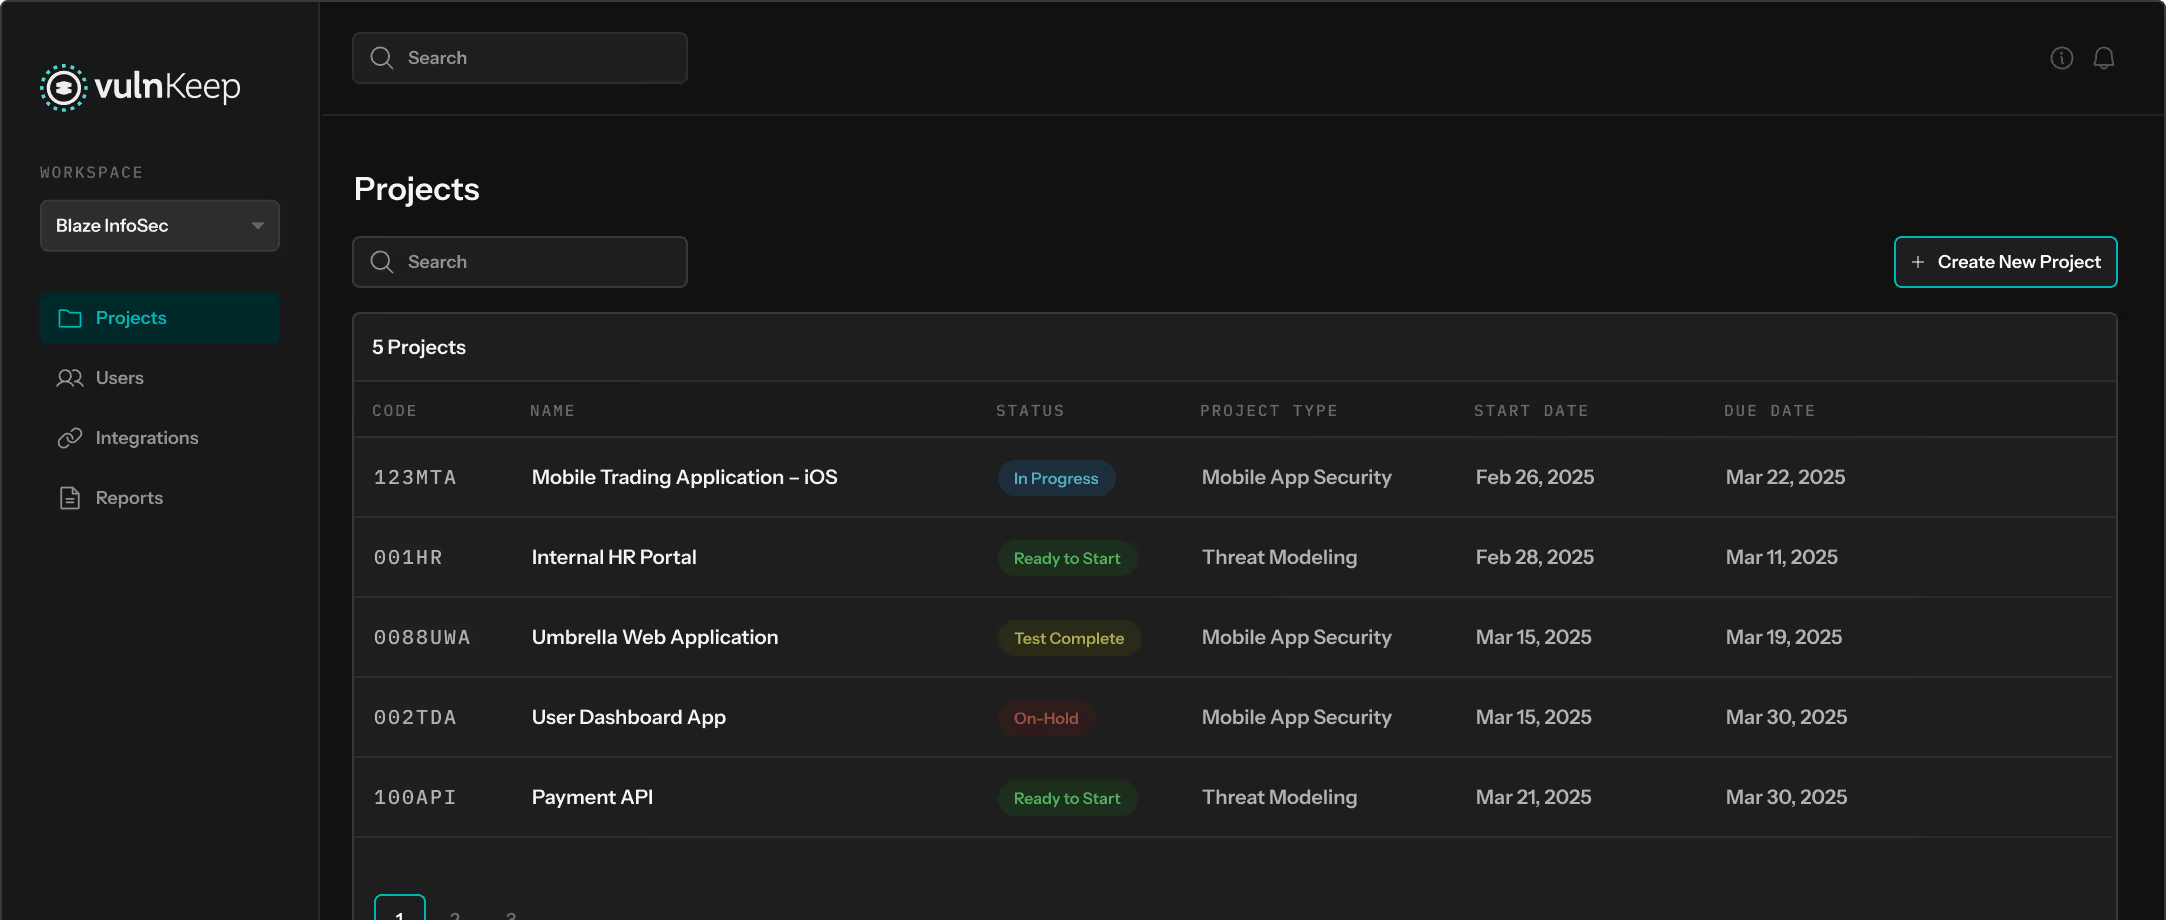
Continuous, on-demand pentesting on one platform, with findings in real time.
Security is a process, not a PDF
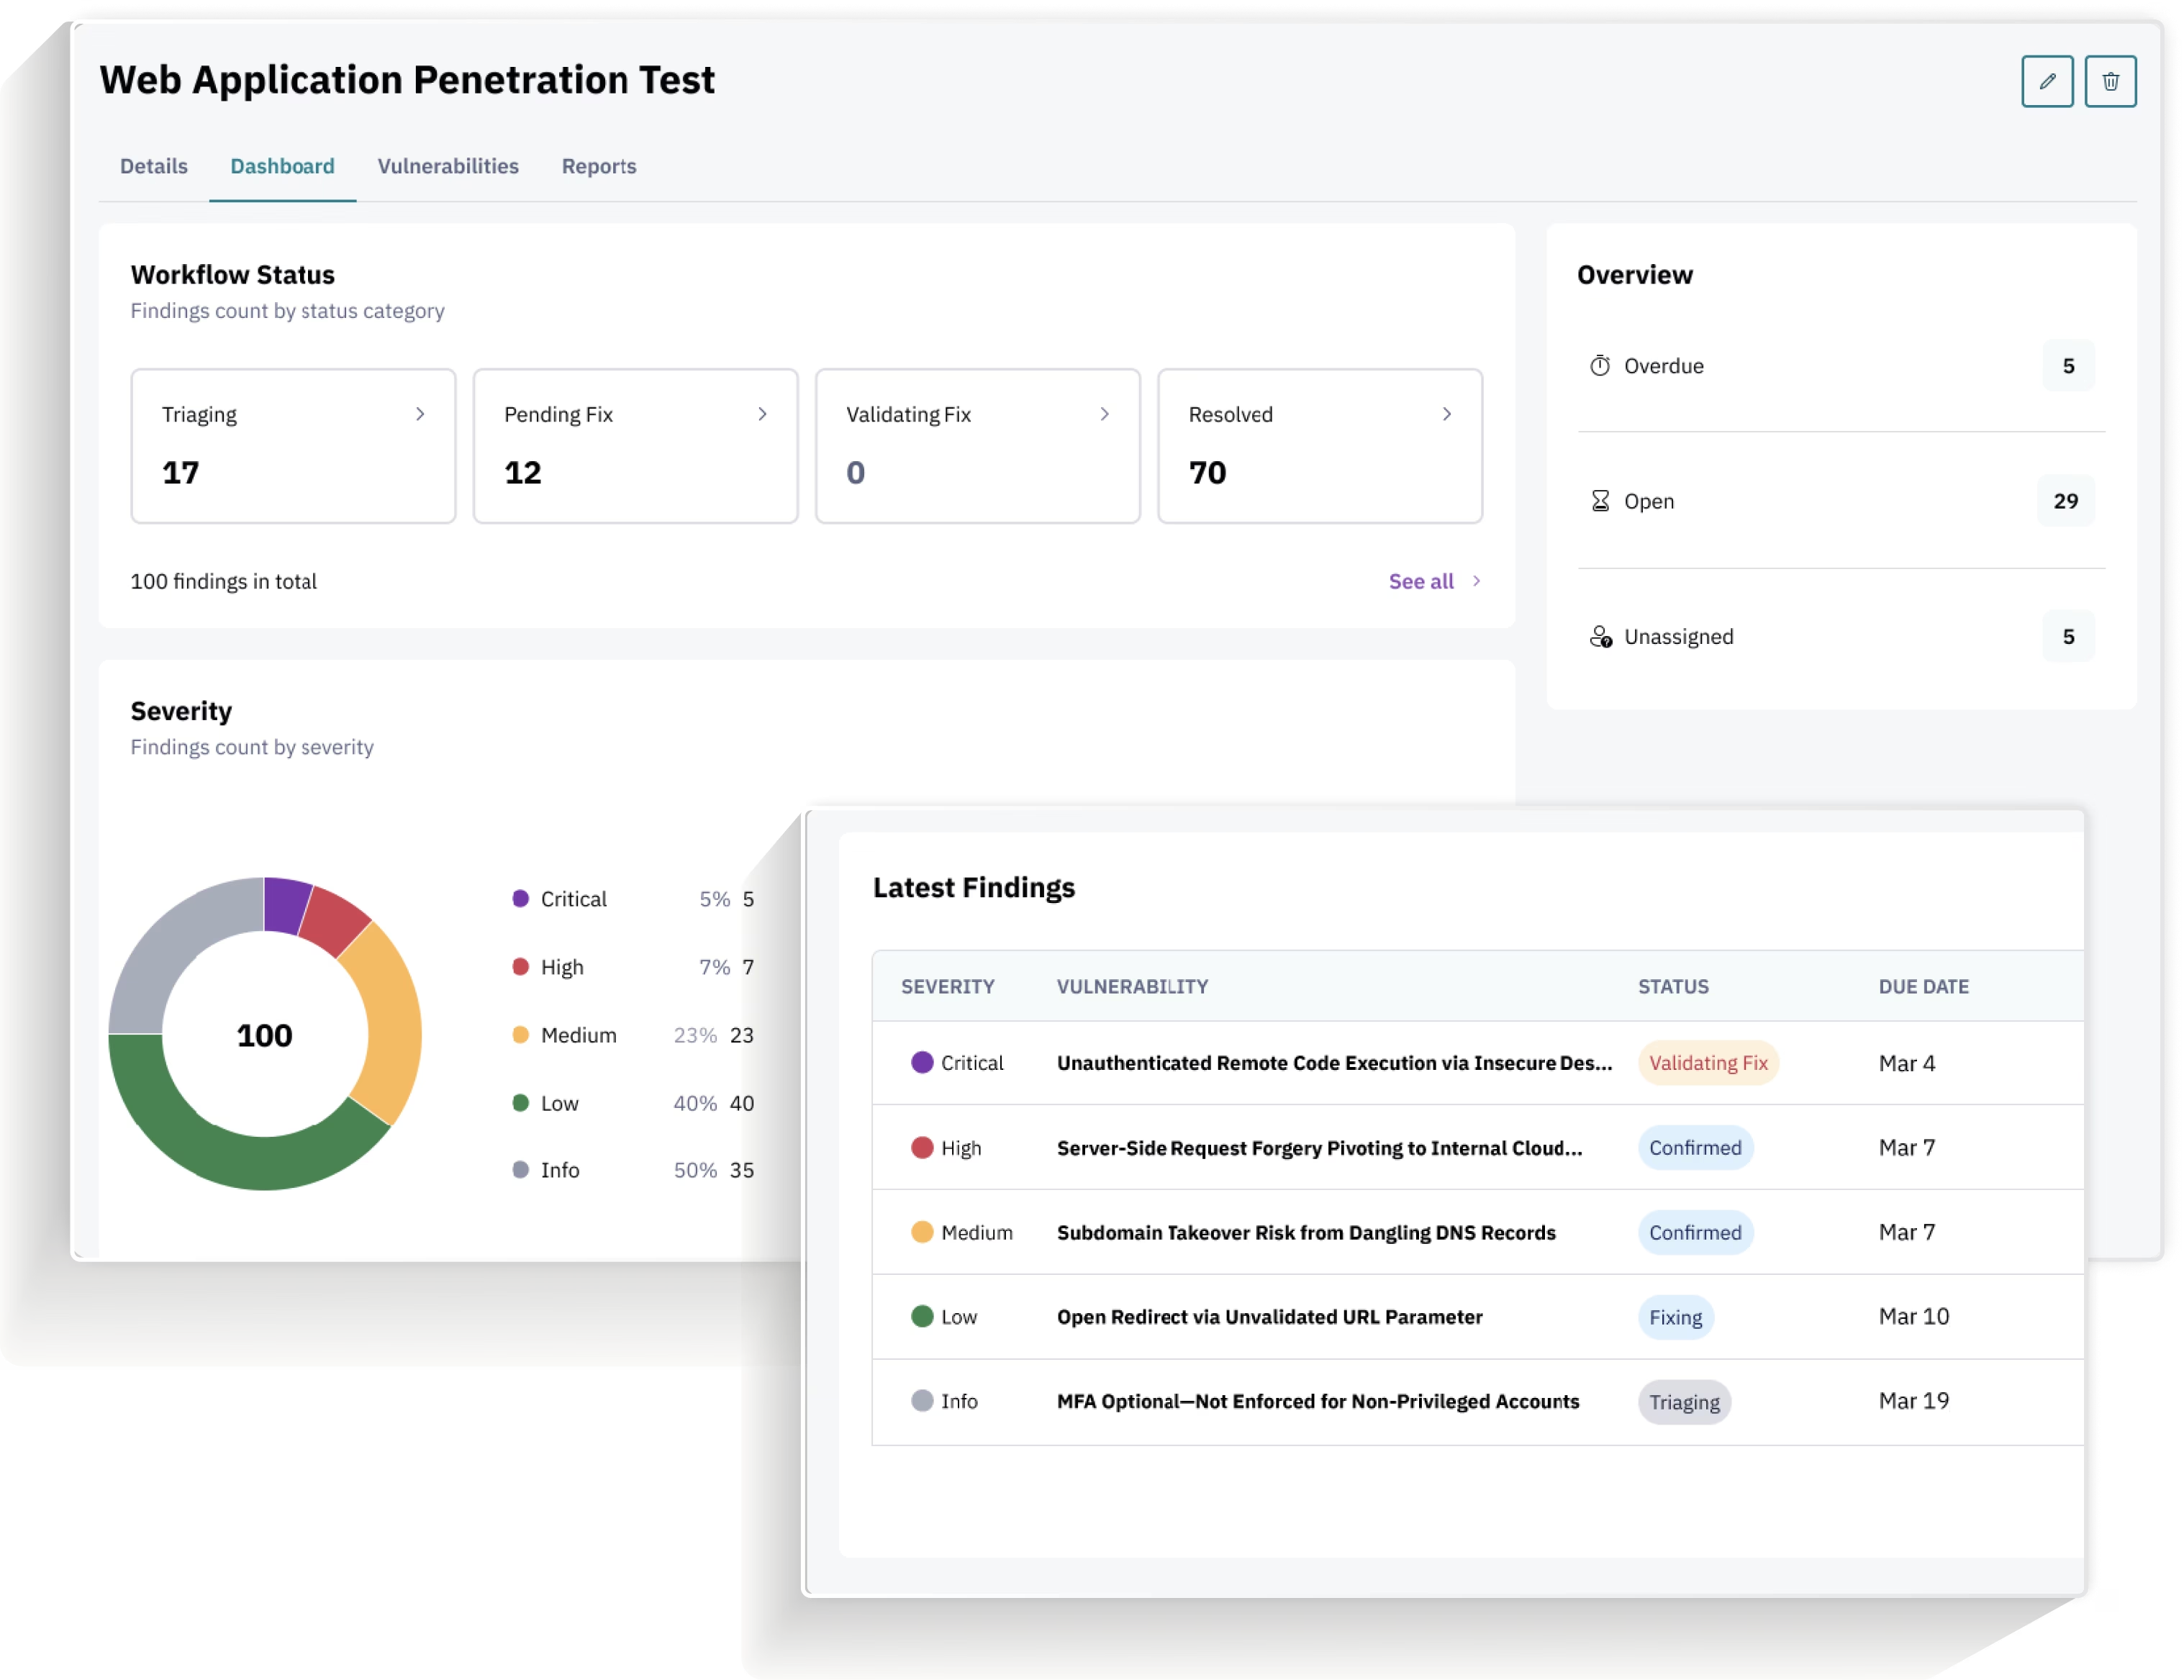
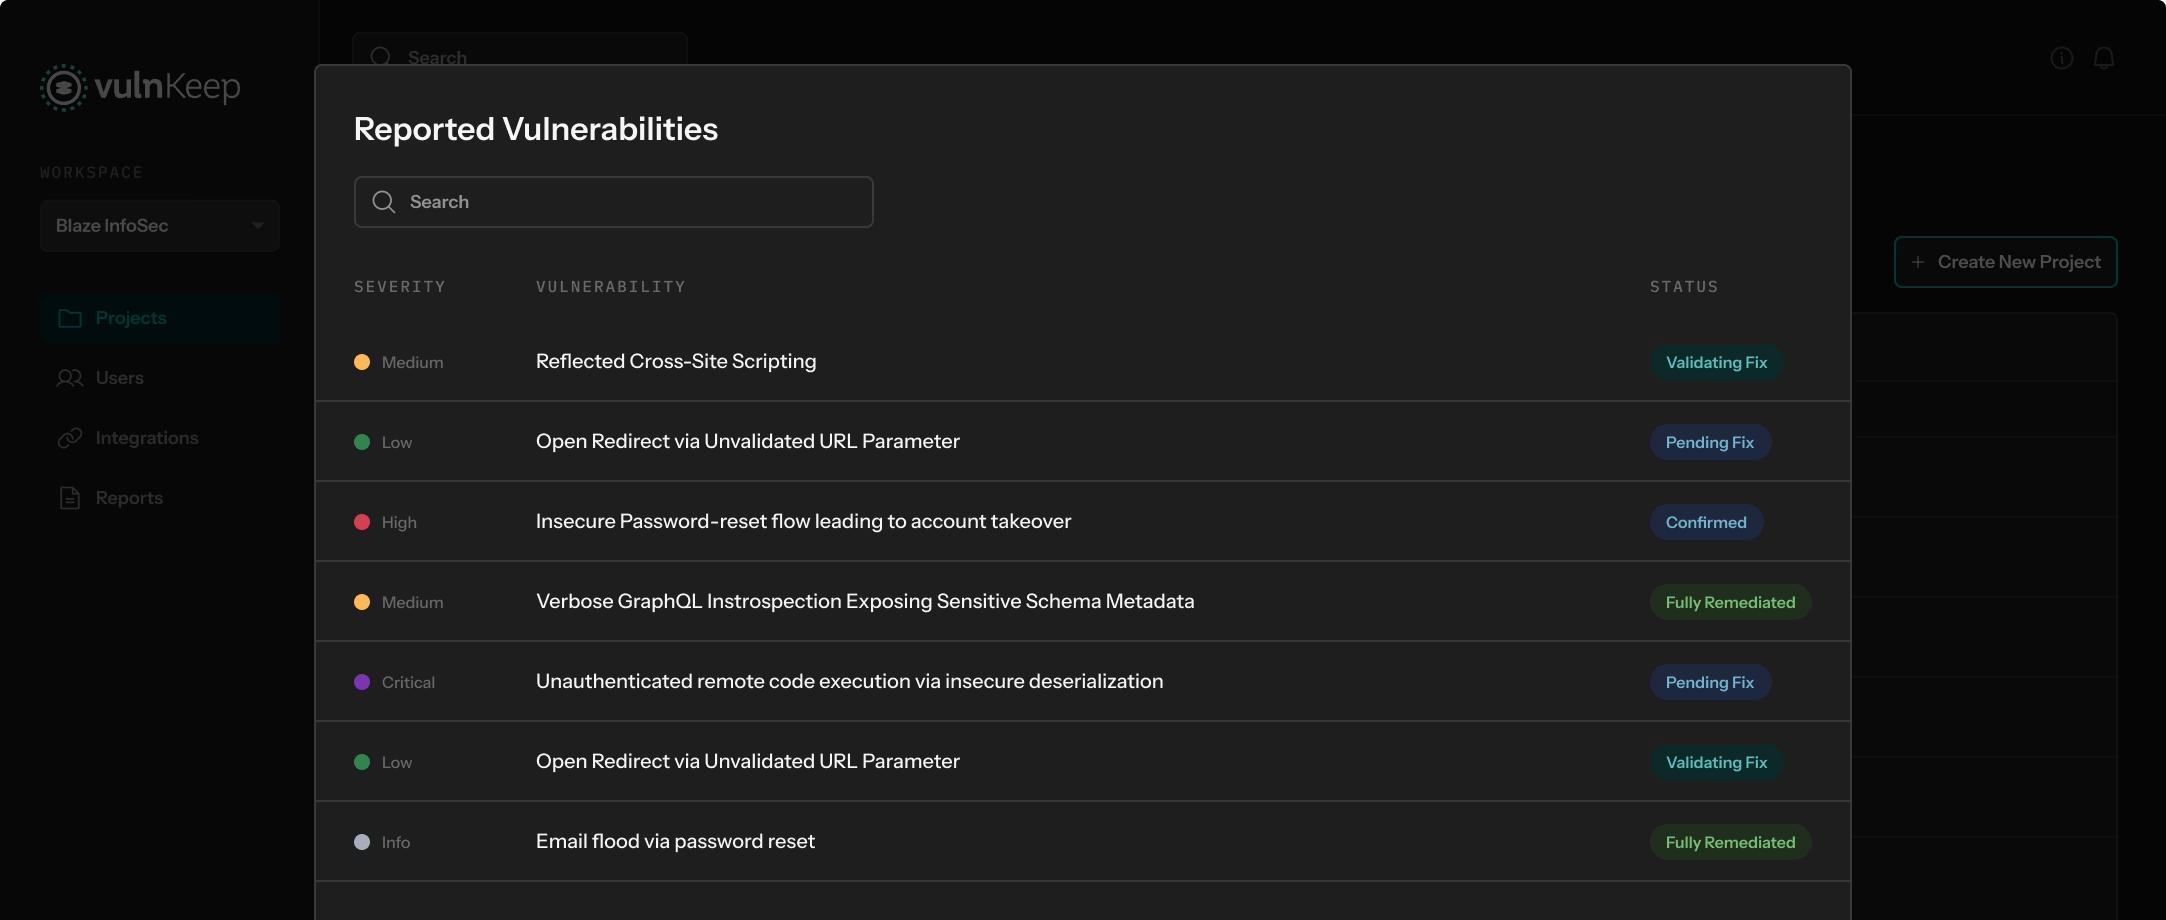
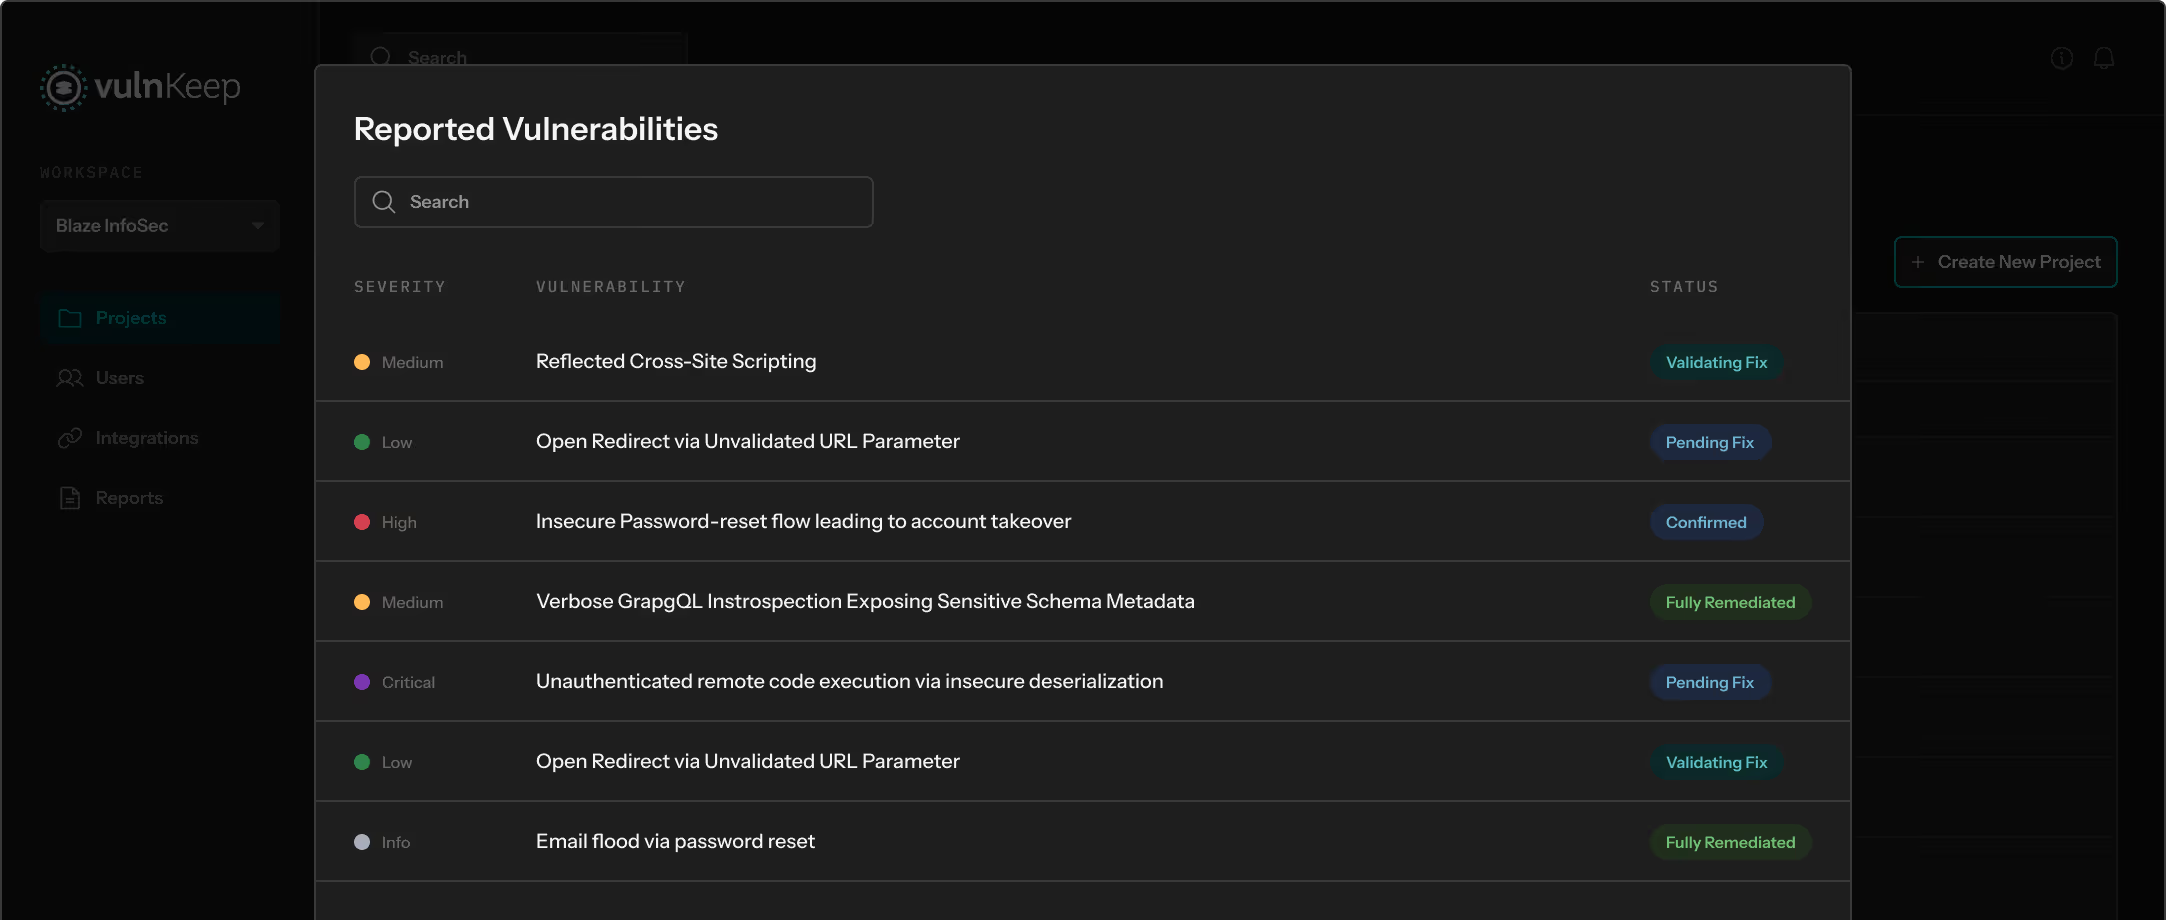
Work directly with the testers, see validated findings in real time, and track remediation and fix validation in one place.



Penetration testing for compliance and beyond
Meet audit, customer, and procurement requirements with independent pentesting and clear, control-mapped reporting—while reducing risk beyond the checkbox.
Why security teams choose Blaze
Senior expertise, direct access, and reporting built for remediation.
Who you work with
A named team of security experts, with direct access from scoping through remediation.
Depth of assessment
Manual, business-logic-aware pentesting enhanced by AI-assisted analysis and shaped by your architecture, attack surface, and risk.
Direct access
Talk directly with the security experts doing the work throughout the engagement.
Remediation support
Get clear guidance, technical answers, and fix validation options based on your engagement.
Reports built for action
Reproduced findings, clear evidence, business context, and control-mapped reporting.
Great collaboration and great findings. Blaze had findings that previous pen tests had missed.
AI expands coverage. Experts validate every finding.
Blaze researchers use AI-assisted analysis to explore more of the agreed scope and reduce repetitive work. Security experts direct the engagement, investigate complex attack paths, and reproduce every reported finding before delivery.

Broader coverage
Assess more endpoints, roles, inputs, and potential attack paths within the agreed scope.

Deeper expert analysis
Keep security experts focused on business logic, exploit chaining, authorization flaws, and product-specific abuse.

Expert-validated findings
Every reported issue is reproduced, reviewed, and assessed in context by a Blaze security researcher before delivery.
Resources for security leaders

Pentest Attestation Letter: What It Is and When You Need One
What a pentest attestation letter includes, when to share it, and how to review one, with a downloadable sample from Blaze.
Penetration Testing Methodology: From Scoping to Retesting
A practical overview of Blaze’s penetration testing methodology, covering the standards, phases, tools, reporting process, and how the approach is adapted to different types of security assessments.
Penetration Testing vs Vulnerability Scanning: What's the Difference?
Discover the differences between penetration testing and vulnerability scanning and which one is best for your company.

Frequently asked questions
Ready to secure what matters most?
Tell us what you need to secure. An expert will help define the right scope and next steps.